Integrating Kimi as a read-only AI security analyst for my homelab SOC

With the new SOC structure and dashboard built, I decided to take on a bigger project: integrating Kimi as a security AI analyst. Its role covers reporting on alerts, examining logs, judging whether something is a false positive, and auditing continuously. It is built in phases, and each phase needs extensive validation before the next one starts. The problem The SOC we built catches things. Seven log sources into Loki, 36 detection rules, alerts routed to my phone by severity, one Grafana dashboard over all of it. ...
8 September 2026 · 10 min
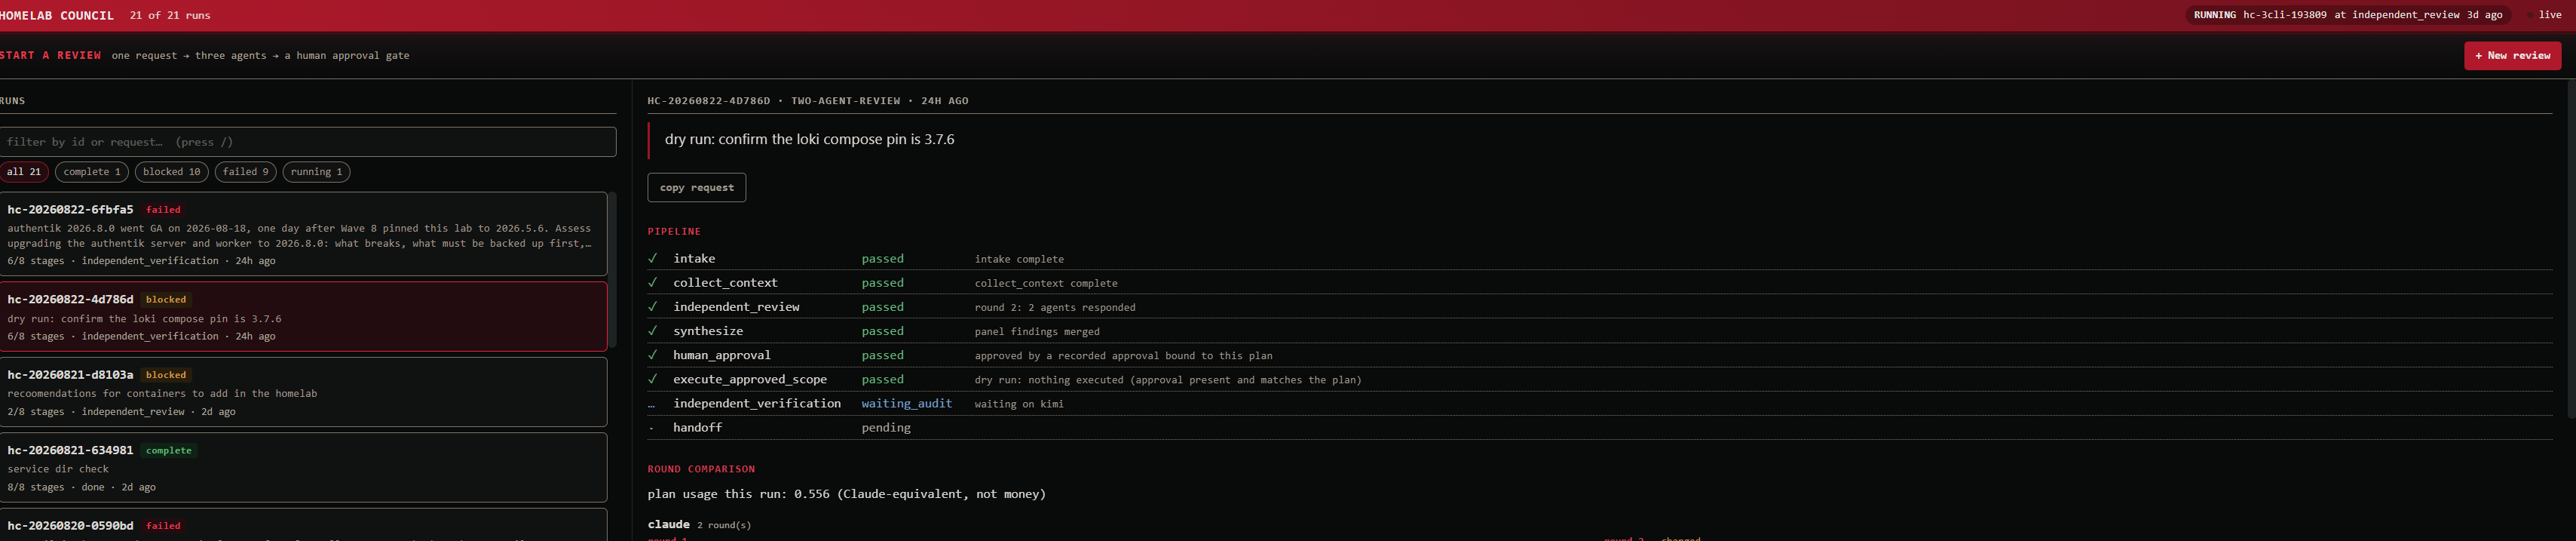
The council dashboard showing a run's pipeline, all stages passed through the approval gate

The Council Gets a Front Door

The council worked. One request went to Claude, Codex and Kimi, they answered independently, and nothing touched the lab without a human approval bound to a hash of the exact plan. It also lived entirely in a terminal, which meant that to approve a run I had to type a run id like hc-20260822-6fbfa5 and then re-type the original 350-character request verbatim, because resume rebuilds the context pack from it. Get one character wrong and you have quietly changed the inputs the agents were judged on. ...

23 August 2026 · 7 min
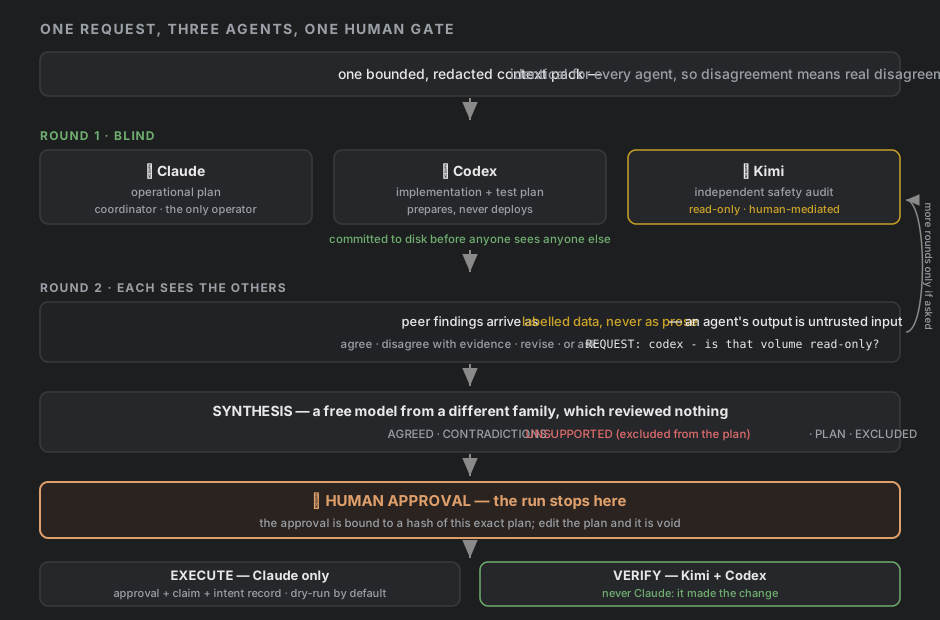
Pipeline diagram: one context pack fans out to Claude, Codex and Kimi in a blind first round, then a peer round, then a free model synthesises, then a human approval gate, then execute and verify

Three Agents, One Approval Gate — Making Claude, Codex and Kimi Review Each Other

I have three coding agents with access to this lab. Claude Code does most of the building. Codex reviews and runs the scans. Kimi audits. Until this week they had never exchanged a word — each got its own context, its own session, and its own chance to be confidently wrong with nobody checking. So I built a thing that makes them work one request together, and put a human approval gate in front of anything that changes the lab. ...

19 August 2026 · 11 min
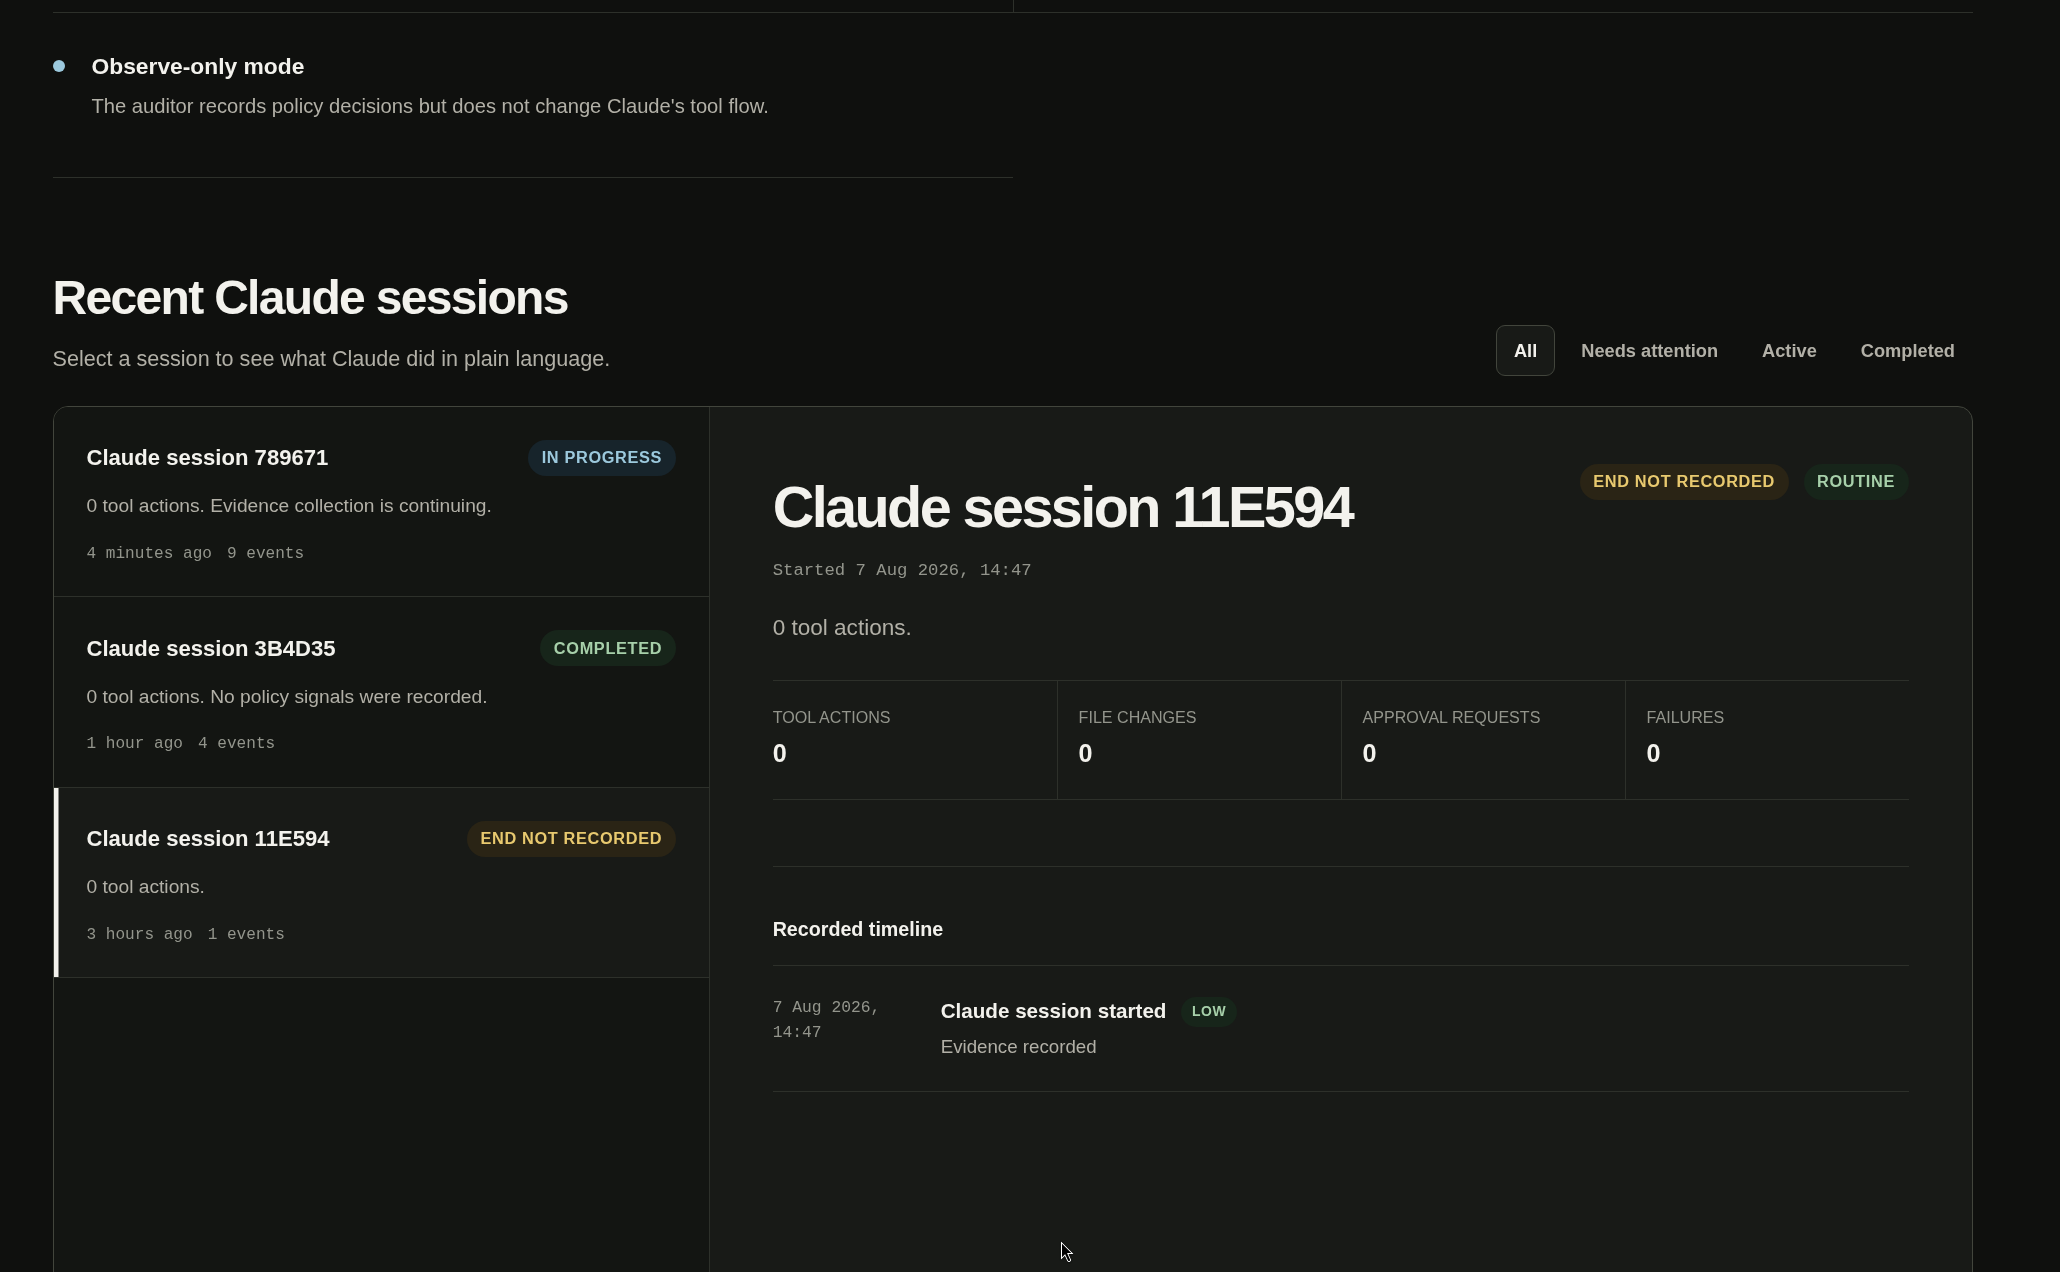
The agent auditor's local operator dashboard, showing observe-only mode and a list of recent Claude sessions with their recorded timelines

Auditing the AI Agent That Runs My Homelab

My homelab has picked up a lot of moving parts this year, and several of them are now LLMs. Claude Code runs natively on the box and does real work against real infrastructure — containers, reverse proxy config, monitoring, the lot. That’s genuinely useful. It also creates a trust problem I hadn’t had before. The problem is simple to state: the same agent that makes a change also writes the summary explaining why the change was safe. That’s convenient. It is not independent verification. If the agent quietly skips a validator and then reports “config validated”, I have no signal at all. The report is the evidence, and the thing that wrote the report is the thing being checked. ...

7 August 2026 · 9 min
RAINBOW MATRIX cover — the post title in rainbow monospace over falling matrix rain on black

A Self-Hosted Multi-LLM Gateway for My Homelab

Claude Code is the main LLM running my homelab. It builds, debugs, and documents most of what happens on the Debian VM. But I wanted to try other models — and give the CLI tools a shared backend — without wiring up a different SDK and API key for every provider. So I put a gateway in front: one endpoint, many models. Claude stays the main driver; everything else is now one config line away. ...

29 July 2026 · 5 min